
How do carders obtain your credit card information online? Learn how carders obtain credit card information online. In this case, there are two possible outcomes: unauthorized or authorized corporate use. To serve your needs, this publication falls somewhere in the middle. You should be aware that obtaining someone’s credit card information without their permission constitutes theft and is thus prohibited.
The point is that, even if their bank opposes the idea, if someone willingly gives you their card information, they trust you enough to do so, which is legal. However, if you are going to use illegal means, you must use any means necessary to obtain the card information. This could indicate that you intend to shop without paying or that you plan to sell or otherwise disclose your card information online in exchange for cash.
Suppose you intend to or merely want to learn how carders/hackers obtain working credit cards online. This publication explains the most commonly used methods out there. Knowing these techniques also helps you protect your card from unauthorized use.
Read: 15+ Websites Where to Shop Online Without an OTP with a Credit Card
How to Obtain Credit Card Information Online
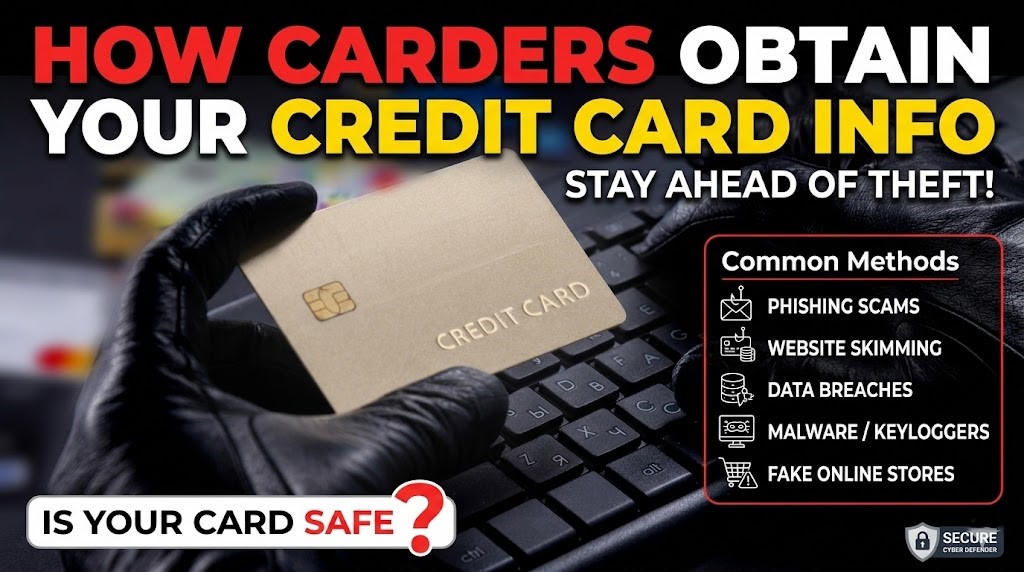
The average person will say, “It’s impossible for someone to know another person’s credit card information.” This is not true; there are numerous online options for doing so, and it occurs on a daily basis. The following are the online ways to obtain credit card information:
1. Online phishing.
You’re most likely already aware of traditional SMS and phone call phishing. You would most likely ignore or report someone if they contacted or sent you a message claiming to be from your financial institution and requesting your credit card information. That’s how intelligent you’ve become.
However, carders have become even smarter. Only a few people still try their luck at phishing via SMS and phone calls. Most people now steal credit card information online through clone websites.
How does this work? Usually in two ways—(1) a fraudster can fake a website or application that looks exactly like your bank’s website or an e-commerce site like Amazon or straight up create an e-commerce website selling items at a too-good-to-be-true price.
The URL of the scam site is then shortened using a link-shortening service like Bitly.com, which is necessary to conceal the fake URL that leads to a cloned site that steals your credentials. Now, when visiting the website, the con artist would have duplicated the login or payment pages to make them appear genuine. When you log in and enter your card information, your information is transferred to the scammer, and you are directed to the main page. You don’t realize what’s going on because it happens so quickly.
Regarding the e-commerce site that sells low-cost items, when you enter your credit card information on the checkout page, the information is compromised, and you frequently never finish entering the information, let alone receiving the item you ordered.
2. Malware and spyware injection.
Technical, but not overly difficult for inexperienced hackers. The typical hacker will convince their victim to install a keylogger on their computer (anyone can be a hacker). Software for keylogging can be downloaded from the internet and installed according to the developer’s instructions.
The target is then instructed to install the keylogger on their system, which the hacker can control remotely whenever a data connection is detected.
The logger will record every keystroke the target makes. The target must typically be coerced into participating in any activity that requires them to enter their credit card information for any reason. After this, the hacker on the other end continues to trace keystrokes until they find the credit card. Other sensitive information, such as credit card information, is also compromised in this situation, as you might expect.
Depending on the hacker, malware injection can be carried out in a variety of other ways. Some people will openly intercept outgoing data, which may contain credit card information, whereas others may exploit compromised browser data.
Read also: List of Cardable Sites (No VBV Sites)
3. RFID skimming.
RFID skimming is not a legitimate way to obtain credit card information online. It does, however, use RFID technology to wirelessly intercept data from credit cards equipped with RFID chips, as well as cell phones and tablets.
RFID skimmers use a near-field communication-enabled device that records unencrypted data from credit cards or a device’s RFID chip to obtain card information such as the cardholder’s name, card number, expiry date, and CVV.
According to IDX, RFID is “a hit-or-miss proposition” and therefore not worth the effort for a carder or hacker. Furthermore, contactless credit cards are encrypted, and most credit card chips do not support RFID.
4. Data breaches.
When sensitive information is removed from a website’s database without the administrators’ knowledge or consent, a breach occurs. Websites that store credit card information are at risk of having it stolen by hackers, as it could happen to both small and large businesses.
The unfortunate part is that the financial institution or e-commerce website may not become aware of the breach for some time. Even if they are aware, they will need some time to fix it. In a short period of time, hackers were able to obtain a large amount of credit card information and money through the dark web.
A data breach is typically quite advanced, necessitating the services of a professional or a team of professionals. It’s also worth noting that it can be disastrous for business. Perhaps one wants to learn how to be a hacker in order to carry out this plan.
5. Compromised public Wi-Fi networks
If a cardholder submits sensitive information such as credit card numbers while connected to a public Wi-Fi network, it may be intercepted if the network is insecure.
A hacker might set up a free public Wi-Fi network and allow anyone to connect to it. The hacker intercepts the target’s device information while they are connected and attempts to entice them to sign on so that they can provide their credit card information. A variety of techniques can be used to intercept Wi-Fi data, including sniffing data packets and man-in-the-middle attacks.
To obtain the connected user’s credit card information, a hacker only needs to be knowledgeable about a specific technique.


Leave a comment