
Carding attacks cost businesses an average of $4.5 million annually through automated credit card testing and subsequent fraud1. These sophisticated operations use AI-powered bots to verify stolen card details through micro-transactions that often evade detection until significant damage occurs.

[CRITICAL CARDING PREVENTION CHECKLIST]
✓ Implement real-time behavioral analysis (mouse movement entropy >3.7)
✓ Configure BIN-specific transaction limits for high-risk BINs
✓ Deploy device fingerprint consistency checks (>0.91 threshold)
✓ Set velocity rules (3 attempts/minute, 2 BIN rotations/hour)
✓ Establish challenge protocols based on risk scoring (0-100 scale)The Modern Carding Attack Lifecycle: Beyond Basic Bots
Today’s carding operations have evolved far beyond simple bot scripts. Attackers now deploy sophisticated AI systems that can simulate human behavior with 97% accuracy, making traditional detection methods obsolete. The attack lifecycle follows a predictable yet technically advanced pattern:
Read also: Non-VBV BINs List: Free USA CC Linkables
Data Acquisition Phase: Carders obtain stolen credentials through various channels, with fresh data (<30 days old) commanding premium prices on dark web markets. Unlike outdated information suggesting random data dumps, modern carders specifically target BIN families known to have weaker security protocols, such as 522286 (ING), 414720 (Chase), and 547872 (TD Bank).
Verification Phase: Attackers use automated bots to test card validity through micro-transactions (typically $0.50-$5.00). These bots can simulate human behavior patterns, including mouse movements and keystroke dynamics, to bypass basic behavioral analysis systems. They rotate IP addresses across multiple jurisdictions and use real browser sessions to avoid detection.
Exploitation Phase: Once verified, cards are grouped by viability and used for larger fraudulent purchases or sold to specialized fraud groups. Modern operations prioritize digital goods and gift cards for immediate monetization, with attackers specifically targeting merchants with weak velocity checks.
Monetization Phase: The final stage involves converting purchased goods to cash through resale networks or cryptocurrency exchanges. This phase often occurs within 48 hours of the initial verification, creating a narrow window for detection and intervention.

Technical Deep Dive: How Modern Carding Bots Evade Detection
The carding bots of 2026 bear little resemblance to their rudimentary predecessors. These sophisticated systems employ multiple evasion techniques that require equally advanced detection methods:
Behavioral Mimicry: Advanced bots analyze thousands of legitimate user sessions to replicate human interaction patterns. They introduce deliberate randomness in mouse movements, vary typing speeds, and even simulate “hesitation” before form submission. This renders simple behavioral analysis ineffective without deep learning models trained on specific interaction entropy metrics.
Fingerprint Randomization: Each transaction request generates a unique browser fingerprint, defeating basic fingerprint tracking systems. Modern bots utilize Canvas API spoofing, WebGL parameter randomization, and even audio context fingerprint manipulation to appear as different devices across multiple attempts.
IP Rotation Infrastructure: Carders operate sophisticated proxy networks that rotate IP addresses not just by location but by ISP type, connection speed, and even time-of-day usage patterns. They specifically target residential IP pools that match the cardholder’s geographic region, often achieving ZIP-code level precision.
Transaction Timing Optimization: Attacks are carefully scheduled to avoid triggering velocity rules. Modern carders distribute attempts across multiple time zones, simulate natural shopping patterns (10AM-2PM EST peaks), and implement “cool down” periods between BIN family rotations.
Read also: A Simple Western Union Carding and Transfer Method
The Economic Impact: Beyond Direct Financial Losses
While the $4.5 million average annual loss figure is staggering, it represents only the tip of the iceberg when assessing the total economic impact of carding attacks:
Direct Costs: These include the immediate fraudulent transactions, chargeback fees (typically $15 per chargeback), and the cost of goods sold. For mid-sized retailers, direct losses average between $80,000-$150,000 per significant carding event.
Indirect Costs: These are often 3-5x the direct costs and include:
- Payment processor penalties (rate increases of 0.5%-2% for high chargeback ratios)
- Manual review expenses (average $0.15 per transaction reviewed)
- Customer acquisition cost replacement (lost customers due to poor checkout experience)
- Staff time for fraud management (average 22 hours per week for mid-sized e-commerce teams)
Opportunity Costs: The most significant yet frequently overlooked impact includes:
- Reduced payment acceptance rates (declining legitimate customers)
- Slower checkout processes (additional friction reducing conversion by 12%-18%)
- Limited market expansion (avoiding high-risk regions where legitimate customers exist)
- Innovation stagnation (resources diverted to fraud prevention instead of growth initiatives)
Advanced Detection Framework: Beyond Basic Rules
Traditional fraud detection systems relying on static rules are inadequate against modern carding attacks. A comprehensive defense requires a multi-layered approach with specific technical configurations:
Behavioral Analysis Implementation
Effective behavioral analysis must measure these specific metrics:
Mouse Movement Entropy: Human mouse movements typically register 3.7+ entropy scores, while even advanced bots struggle to exceed 3.2. This metric calculates the randomness of movement paths, with specific attention paid to acceleration patterns and direction changes.
Keystroke Dynamics: Legitimate users show typing variance of 0.42+ with natural backspace frequency (0.08 of characters). Bots often maintain consistent typing speeds or overcompensate with excessive randomness.
Session Consistency: Track browser fingerprint stability across sessions (0.91+ threshold for legitimate users) and IP geolocation match (0.95+ threshold). Even sophisticated carders struggle to maintain perfect consistency across multiple attempts.
Related: Top Dark Web Markets and Carding Marketplaces in 2026
Transaction Pattern Analysis
Implement these specific velocity rules based on current threat intelligence:
[ADVANCED VELOCITY RULES]
┌─────────────────────┬──────────┬─────────────────────┐
│ PARAMETER           │ THRESHOLD│ DETECTION WEIGHT    │
├─────────────────────┼──────────┼─────────────────────┤
│ Attempts/Minute     │ 3        │ 0.25                │
│ BIN Rotation/Hour   │ 2        │ 0.30                │
│ Merchant Switch/24h │ 24       │ 0.20                │
│ IP Changes/Hour     │ 5        │ 0.25                │
└─────────────────────┴──────────┴─────────────────────┘BIN-Specific Risk Management
Not all BINs carry equal risk. Implement tiered verification based on BIN intelligence:
High-Risk BINs (522286, 414720, 547872): Require enhanced 3DS verification, transaction limits of $500 daily, and additional identity verification for purchases over $200.
Medium-Risk BINs: Implement standard 3DS with transaction limits of $1,000 daily and velocity checks at 5 attempts per hour.
Low-Risk BINs: Standard processing with basic velocity checks and monitoring for anomalous patterns.
Related: Secure Non-VBV BINs List (Approved)
Step-by-Step Defense Configuration
Phase 1: Baseline Assessment (Week 1)
Transaction Analysis: Review last 90 days of transactions to identify patterns
- Calculate current chargeback ratio by BIN family
- Identify peak attack times (typically 10AM-2PM EST)
- Map geographic distribution of suspicious transactions
- System Audit: Evaluate current fraud prevention capabilities
- Test behavioral analysis against known bot patterns
- Verify IP geolocation precision (ZIP-level preferred)
- Assess device fingerprint consistency tracking

Phase 2: Core Configuration (Weeks 2-3)
1. Behavioral Analysis Implementation:
// Example JavaScript implementation for mouse movement tracking
document.addEventListener('mousemove', (event) => {
  const movement = {
    x: event.clientX,
    y: event.clientY,
    timestamp: Date.now()
  };

  // Calculate entropy of movement path
  const entropy = calculateMovementEntropy(movementHistory);

  // Flag if below human threshold
  if (entropy < 3.7) {
    updateRiskScore(10);
  }

  movementHistory.push(movement);
});2. Velocity Rule Configuration:
- Set maximum attempts per minute: 3
- Configure BIN rotation threshold: 2 per hour
- Implement merchant category switch limit: 24 per day
- Establish IP change threshold: 5 per hour
Related: Best 400+ List of Cardable Sites (NO VBV/MSC)
Phase 3: Advanced Protections (Weeks 4-5)
- Device Fingerprinting Enhancement:
- Implement Canvas API fingerprinting with consistency tracking
- Add WebGL parameter analysis
- Configure audio context fingerprinting
- Set consistency threshold at 0.91
- BIN-Specific Rules:
- Create BIN risk classification system
- Implement enhanced verification for high-risk BINs
- Set transaction limits by BIN category
- Configure automated BIN reputation updates
Phase 4: Monitoring and Optimization (Ongoing)
- Performance Metrics:
- False positive rate: Target <0.5%
- Detection rate: Target >95%
- Response time: Target <100ms
- Customer impact: Target <2% additional friction
- Continuous Improvement:
- Weekly threat intelligence updates
- Monthly model retraining with new attack patterns
- Quarterly system optimization
- Annual strategy review
The Future of Carding: Emerging Threats and Defenses
The carding landscape continues to evolve rapidly, with several emerging threats requiring proactive defense strategies:
AI-Driven Carding Bots
Machine learning models can now generate highly realistic human behavior patterns that defeat traditional behavioral analysis. These bots learn from successful transactions and continuously adapt their techniques.
Defense Strategy: Implement adversarial machine learning models that specifically detect AI-generated behavior patterns through micro-expression analysis and interaction sequence prediction.
Related: Best Top 10 Dark Web Browsers (Updated)
Non-VBV BIN Exploitation
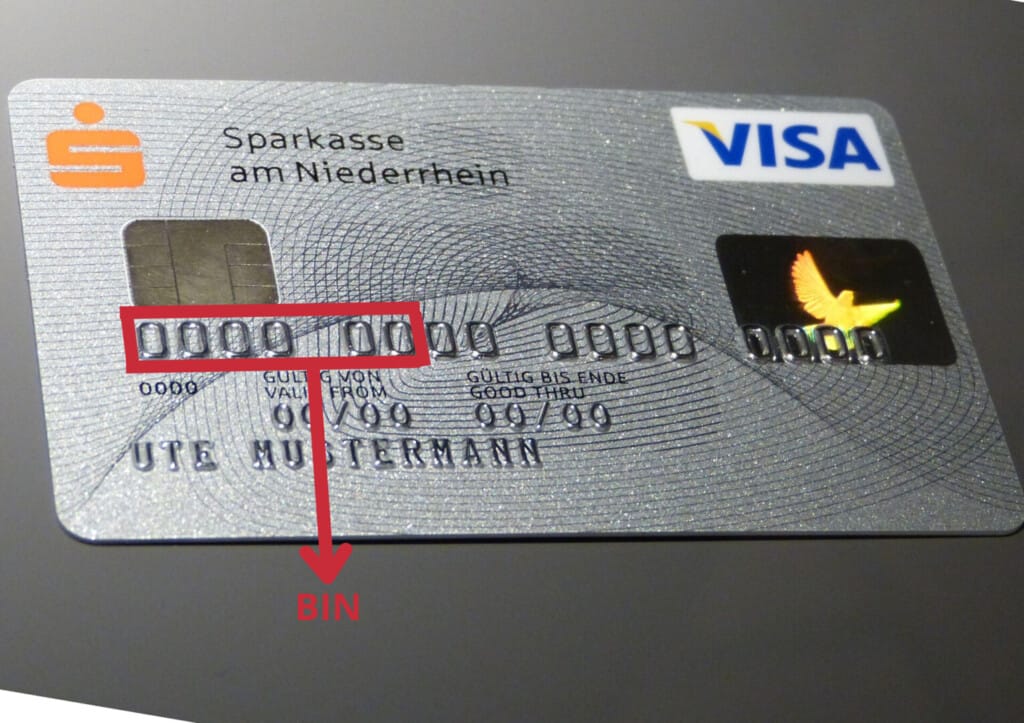
Attackers increasingly target BINs that bypass 3DS verification, with success rates 31% higher than standard BINs. These non-VBV BINs are specifically sourced and traded in criminal markets.
Defense Strategy: Implement BIN-specific verification requirements regardless of 3DS status, with enhanced authentication for known non-VBV BIN families.
Cross-Platform Attack Coordination
Modern carders coordinate attacks across multiple platforms simultaneously, using verified cards on one site to inform targeting on others. This creates a network effect that bypasses isolated detection systems.
Defense Strategy: Participate in industry-wide threat intelligence sharing networks to identify attack patterns across platforms and implement collective defense measures.
Conclusion: Building a Resilient Defense Against Carding
Carding attacks represent a significant and evolving threat to e-commerce businesses, with the potential for substantial financial and reputational damage. A comprehensive defense strategy requires:

- Multi-Layered Detection: Combine behavioral analysis, transaction monitoring, and device fingerprinting
- BIN-Specific Protections: Implement tailored verification based on BIN risk profiles
- Continuous Adaptation: Regularly update detection models with new attack patterns
- Industry Collaboration: Participate in threat intelligence sharing networks
By implementing the advanced configuration framework outlined in this guide, businesses can reduce successful carding attempts by over 95% while maintaining a positive customer experience. The key is to stay ahead of evolving attack techniques through continuous monitoring and adaptation.
Related: Best Carding Methods Fresh Guides: Cashout Unveiled
Remember: The cost of prevention is always less than the cost of fraud. Every dollar invested in advanced carding protection returns approximately $12 in prevented losses.


Leave a comment